Your compliance team is juggling spreadsheets, email approvals, and audit requests. Some tools promise automation but leave you exporting evidence by hand when a regulator asks for proof. That gap is usually what pushes teams to start comparing platforms.
This article breaks down what regulated businesses should demand from compliance workflow software, then reviews eight options, including Process Street, Vanta, Scrut Automation, LogicGate Risk Cloud, Onspring, Diligent, Secfix, and Zyphe. You will finish with concrete selection criteria and a clear pick for best overall.
What to Look For in Compliance Workflow Software for Regulated Businesses
Selecting compliance workflow software for a regulated business requires evaluating more than just workflow automation-it demands a platform that can enforce policies, maintain audit trails, and adapt to frameworks like HIPAA, GDPR, SOX, and FDA 21 CFR Part 11.
A generic task manager will not survive a regulatory examination. Compliance officers need evidence, not just completed checklists. The criteria below separate tools built for regulatory compliance from those that merely happen to be used by compliance teams.
- Regulatory framework support. The platform should map controls to named frameworks. A bank preparing for SOX needs internal controls over financial reporting documented and testable. A hospital needs HIPAA-aligned incident tracking. A life sciences firm needs FDA 21 CFR Part 11 audit trails for electronic records. A payment processor needs PCI DSS evidence collection. Look for templates or control libraries tied to HIPAA, GDPR, SOX, PCI DSS, ISO 27001, and 21 CFR Part 11 rather than a blank canvas.
- Audit trail and version control. Every change to a policy, approval, or record should be timestamped and attributed to a named user. In pharmaceutical compliance, reviewers must see who edited a controlled document, when, and what the prior version said. Without immutable version history, document control collapses during an inspection.
- Policy management and enforcement. Writing a policy is easy. Proving it was acknowledged, applied, and enforced is the hard part. The software should route policies for review, collect attestations, and trigger workflows when a policy applies to a specific process.
- Risk assessment and scoring. A GRC platform should let teams score risks by likelihood and impact, then link each risk to mitigating controls. Financial services firms use this to prioritize remediation across business units.
- Incident management and CAPA workflows. Healthcare compliance teams need to log an incident, investigate root cause, assign a corrective action, and verify effectiveness. CAPA workflows should close the loop automatically rather than relying on email follow-up.
- Electronic signatures and access controls. Role-based permissions and 21 CFR Part 11 compliant e-signatures matter anywhere records carry legal weight. Legal compliance teams also need granular control over who can view privileged material.
- Integration with existing systems. Compliance data rarely lives in one place. Connections to ERPs, HRIS platforms, ticketing systems, and document repositories keep evidence current without manual re-entry.
- Data governance and residency options. GDPR requires knowing where personal data is stored and processed. Some regulated businesses need regional hosting or data residency guarantees before a vendor can be approved.
- Reporting and analytics. Compliance officers need dashboards that show control status, open incidents, overdue reviews, and audit readiness at a glance. Regulatory reporting should be exportable, not reconstructed by hand.
- Scalability for multi-site operations. A single-site tool breaks when a company operates across regions, each with its own regulator. Multi-site support means shared templates, local variations, and consolidated oversight.
Weigh these criteria against your specific regulatory requirements rather than a generic feature checklist. A healthcare provider and an investment bank will rank them differently, and the right compliance management platform is the one that matches your highest-stakes obligation first.
1. Process Street - Best Overall
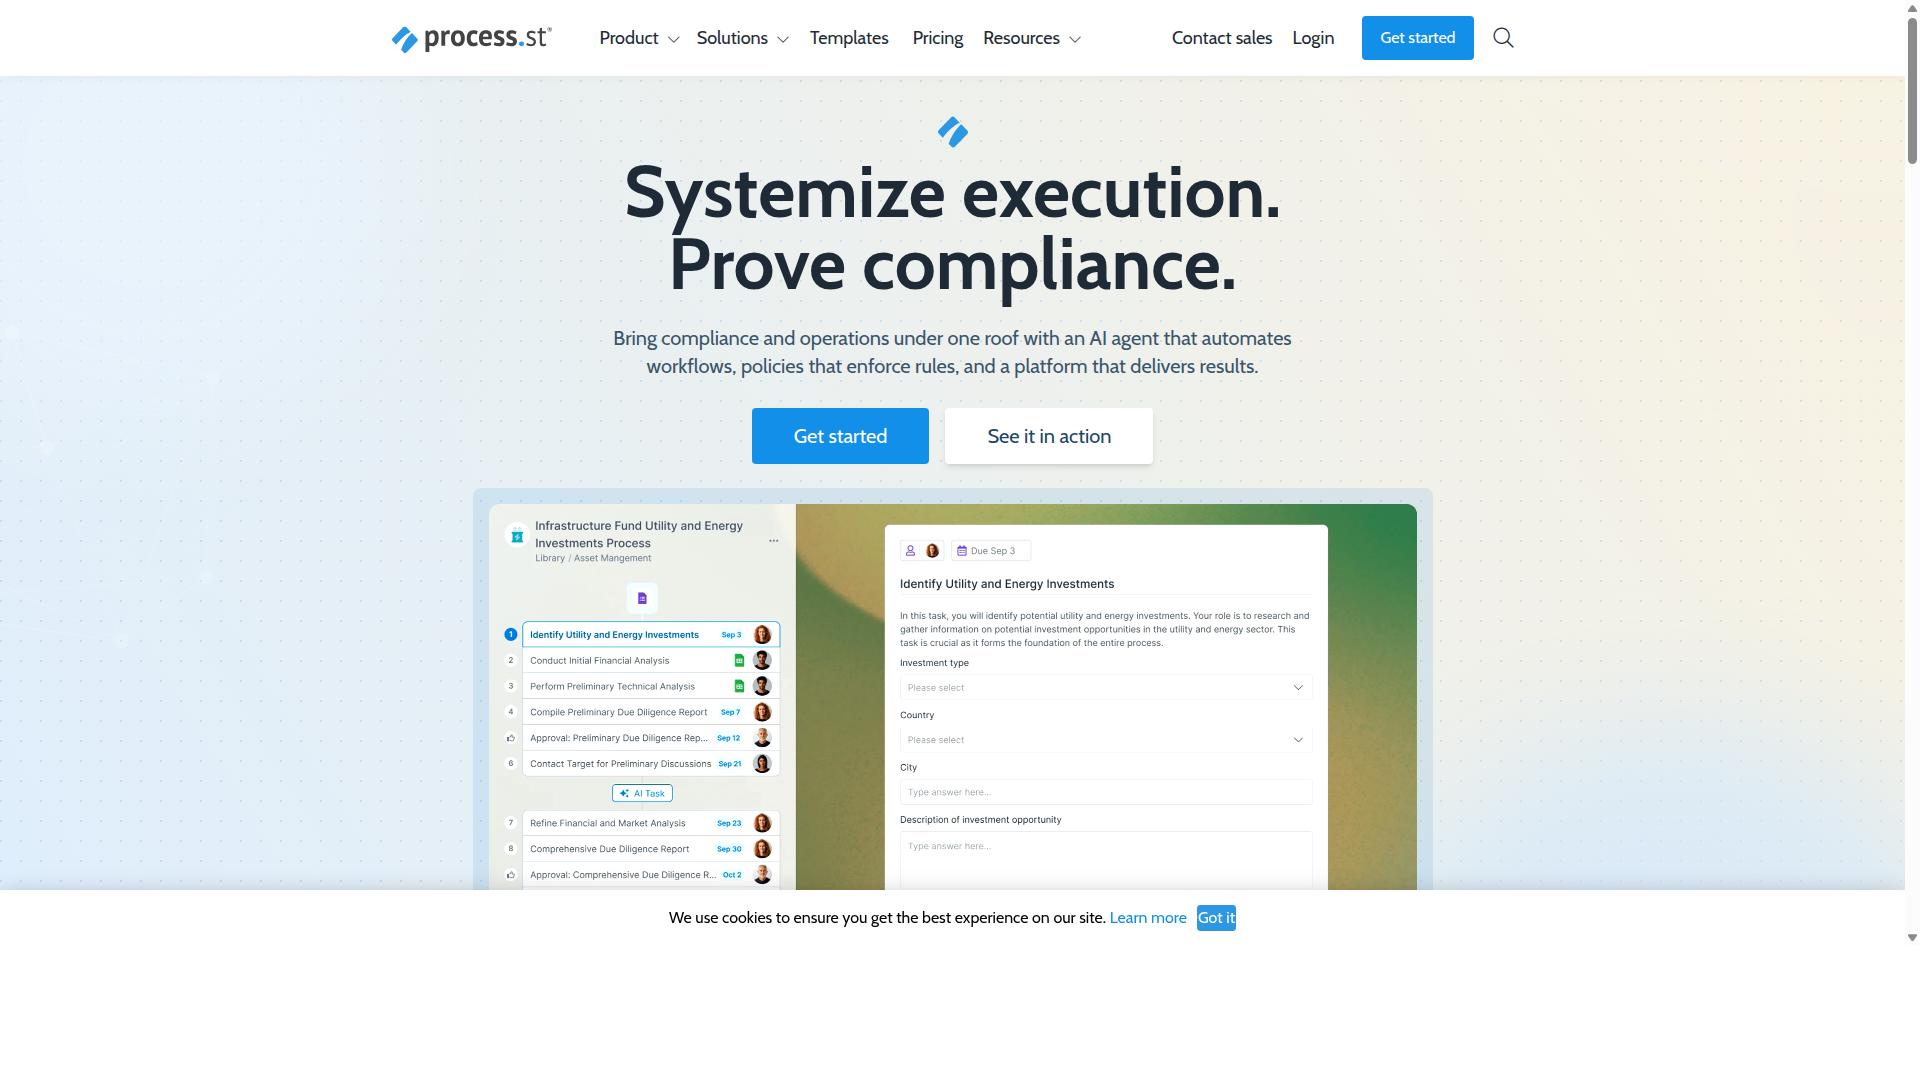
Process Street stands out as the best overall compliance workflow software for regulated businesses by combining document management, workflow automation, and audit-ready proof in a single platform trusted by over 3,000 companies and 1 million users.
The platform brings together Docs, Ops, and Cora to help teams automate business processes, enforce policies, and produce audit-ready evidence. It is available globally with data residency options in the US, UK, Canada, EU, Australia, and UAE, and holds SOC 2 Type II and ISO 27001 certifications.
Teams in Operations, Customer management, Compliance, Human resources, Finance, IT and security rely on it across financial services, real estate, manufacturing, healthcare, professional services, and technology. Salesforce, Colliers, and HEALTHeLINK™ are among the organizations that use Process Street for their compliance operations.
Key Features, Products, and Pricing
Process Street offers three core products, Docs, Ops, and Cora, that together cover document management, policy control, and AI-powered workflow automation, with pricing plans designed for startups through enterprises.
Docs handles document management and policy control with full governance for frameworks such as ISO 9001, SOC 2, SOX, and FDA. This gives compliance officers a central place to manage policy management, version control, and document control, which are foundational for audit trail integrity and regulatory reporting.
Ops delivers workflow automation and process orchestration that turns policies into AI-powered workflows. For regulated businesses, this means internal controls move from static documents into repeatable tasks that support corrective action, CAPA, and incident management. Access controls and electronic signatures help teams keep data governance intact across every step.
Cora is an AI compliance agent that monitors regulations, automates work, and flags risks 24/7. It supports continuous compliance monitoring so that regulatory requirements do not slip through gaps between reviews. Together with platform features like Process AI, Automations, Analytics, Apps, and Integrations, these products form a practical governance risk and compliance foundation.
Integrations include Zapier, Microsoft Power Automate, Tray.io, Make, and Public API access, so compliance workflow software can connect to the systems a business already uses.
Pricing follows three tiers:
- Startup: A simplified Pro plan for startups with unlimited workflows and tasks, up to 5,000 Data Set records, 5 users, 10 guests, 10 automation apps, 100 automation actions per month, and Public API (50 calls per month).
- Pro: Transform team knowledge into actionable workflows with unlimited workflows and tasks, up to 10,000 Data Set records, custom users and guests, all automation apps, custom automation actions per month, and custom API calls per month.
- Enterprise: A scalable operational knowledge repository with custom Data Set records, unlimited Public API access, a dedicated Success Manager, priority support, fully-managed workflows, custom integrations, bulk document import, process consulting and health audit, and personalized team training.
A 14-day free trial is available on the Pro plan with no credit card required. For regulated businesses weighing value, IMCD UK reported 30% faster documentation and a reduction of over 75% in setup time, showing how process orchestration can translate directly into operational efficiency.
2. Vanta
Vanta is a well-known compliance automation platform that helps businesses achieve and maintain frameworks like SOC 2, ISO 27001, and HIPAA, primarily through automated evidence collection and continuous monitoring. It has become a common starting point for technology companies that need to demonstrate security posture to customers and auditors without building a compliance program from scratch.
Rather than treating compliance as a periodic project, Vanta is built around continuous control monitoring. It connects to a company's existing cloud infrastructure, identity providers, and developer tools, then checks whether configured controls still meet the requirements of a given framework. When something drifts, the platform surfaces it, which helps compliance officers catch gaps before an audit rather than during one.
Core capabilities
Vanta's feature set centers on reducing manual work in audit preparation and ongoing compliance monitoring:
- Automated evidence collection pulls configuration and activity data from connected systems, reducing screenshots and spreadsheet tracking.
- Continuous control monitoring evaluates controls on an ongoing basis instead of at a single point in time.
- Third Party Risk Management supports vendor review and tracking of external risk exposure.
- Trust Center gives a public-facing view of security posture for prospects and partners.
- Security questionnaire automation helps teams respond to buyer due diligence requests.
- AI Governance and Vanta AI capabilities extend coverage to emerging areas of risk and oversight.
The platform supports a broad set of frameworks, including SOC 2, ISO 27001, ISO 42001, GDPR, HIPAA, and HITRUST, and connects to more than 400 integrations. That breadth makes it practical for organizations that need to satisfy several regulatory requirements at once, particularly where overlapping controls can be mapped to more than one standard.
Where Vanta fits well
Vanta is commonly used by startups, mid-market companies, and enterprise teams, with notable adoption in healthcare, fintech, and government-adjacent sectors. For a SaaS company preparing for its first SOC 2 report, or a fintech firm that needs to show customers it handles data responsibly, the automation-first model can shorten the path to an initial certification and make renewals less painful.
The value is strongest when a company's controls are largely technical and tied to cloud infrastructure. In those environments, evidence can be gathered programmatically and audit trail data accumulates without manual intervention. Teams also tend to appreciate the Trust Center, since it turns compliance work into something sales and marketing can actually use during deals.
For organizations weighing a GRC platform, Vanta is worth evaluating when the primary goal is certification readiness and security posture visibility. It is less obviously a fit when the core problem is operational process control rather than technical control monitoring.
Potential limitations for regulated businesses
Vanta's strengths are concentrated in security and privacy frameworks. Businesses in heavily regulated sectors often carry obligations that extend well beyond those boundaries, and this is where the platform may be better suited as one part of a broader compliance stack rather than the whole of it.
Several areas deserve scrutiny during evaluation:
- Operational workflow automation for day-to-day business processes is not the platform's central focus, so teams expecting to model approvals, handoffs, and recurring procedures may find it limited.
- CAPA management and structured corrective action tracking, which matter in pharmaceutical and medical device contexts, are not core capabilities.
- Frameworks such as FDA 21 CFR Part 11, SOX, and PCI DSS bring requirements around document control, version control, and electronic signatures that go past monitoring and into process execution.
- Incident management and risk assessment workflows may need dedicated tooling if they must feed into formal quality or safety systems.
- Data governance and regulatory reporting obligations in financial services and healthcare compliance often demand record-keeping depth that sits outside a certification-focused tool.
None of this makes Vanta a weak product. It reflects a deliberate focus. For a regulated business, the practical question is whether certification automation covers the majority of your obligations or only the security-facing slice. Where internal controls must be evidenced through repeatable operational processes, pairing a monitoring tool with dedicated compliance workflow software is often the more durable approach.
Buyers should also confirm framework coverage against their specific regulator, check that required integrations exist for their environment, and map every obligation to a feature before committing. Publicly available documentation and a trial or demo are the most reliable ways to test that fit.
3. Scrut Automation
Scrut Automation is a compliance automation platform designed to streamline security and privacy compliance for cloud-native companies, with support for frameworks such as SOC 2, ISO 27001, GDPR, and HIPAA. It centralizes the evidence collection and control monitoring work that typically slows down audit preparation.
The platform is built around continuous monitoring rather than point-in-time snapshots. Instead of scrambling before an audit, teams can track control status on an ongoing basis and address gaps as they appear.
Beyond core compliance automation, Scrut Automation covers risk management and vendor risk assessment. This makes it a reasonable fit for SaaS and technology companies that need to demonstrate security posture to enterprise buyers or investors.
Scrut Automation supports a range of frameworks relevant to regulated businesses, including:
- SOC 2
- ISO 27001
- HIPAA
- GDPR
- PCI DSS
- NIST AI RMF
The platform also provides continuous runtime security, asset inventory tracking, user privilege validation, employee training, and third-party risk assessment. These capabilities map well to security-focused compliance programs where evidence gathering and control validation are the primary bottlenecks.
Scrut Automation serves startups, growth-stage companies, and enterprises across industries such as enterprise software, financial services, healthcare, travel, and education. Pricing is not publicly disclosed, so buyers should request a quote based on their framework count and company size.
For regulated businesses, Scrut Automation's strength lies in security and privacy compliance. It handles the evidence trails, control monitoring, and audit preparation that frameworks like SOC 2 and ISO 27001 demand.
Where it may fall short is in broader operational workflow automation. Teams looking for a GRC platform that also manages internal controls, corrective actions, document control, and cross-departmental processes may find the scope narrower than expected.
Industry-specific regulations such as FDA 21 CFR Part 11 for pharmaceutical compliance, or SOX internal controls for public companies, are not the platform's primary focus. Organizations in those spaces should verify framework coverage carefully before committing.
Scrut Automation is a credible option for technology companies prioritizing security certifications. Regulated businesses with heavier operational or industry-specific requirements should weigh whether a dedicated compliance workflow tool better fits their needs.
4. LogicGate Risk Cloud
LogicGate Risk Cloud is a flexible GRC platform that enables organizations to build custom risk and compliance workflows, making it suitable for complex regulatory environments in finance, healthcare, and other regulated sectors. It is best understood as a workflow automation platform for risk management rather than a fixed, out-of-the-box compliance tool.
That distinction matters for compliance officers evaluating compliance workflow software. LogicGate gives teams the building blocks to design their own processes, which appeals to organizations whose regulatory requirements do not fit neatly into a standard template.
Key capabilities reported for the platform include:
- Drag-and-drop workflow design for building and automating risk and compliance processes without heavy coding
- Customizable risk assessments that teams can shape around their own risk frameworks and internal controls
- Real-time dashboards for monitoring workflow status and compliance activity
- Automated notifications that keep owners informed as tasks move through a process
- Audit trails that record activity for review and evidence gathering
- Integrations with existing systems so risk data can connect to the tools teams already use
Together, these features support several core governance risk and compliance functions. Policy management, incident management, and regulatory reporting can all be handled through configurable workflows rather than disconnected spreadsheets and email threads.
For financial services teams working under SOX or PCI DSS, or healthcare organizations navigating HIPAA, that configurability is a genuine advantage. The platform is designed for organizations that need structured risk and compliance processes and want to adapt them as regulations shift.
The trade-off is setup effort. Because LogicGate is a build-it-yourself environment, workflow automation depends on how well a team designs its own processes. Smaller compliance teams without dedicated administrators may find the initial configuration demanding, and the platform is generally positioned toward organizations with the resources to invest in that build-out.
Cost is a related consideration. LogicGate does not publish pricing on the pages reviewed here, so buyers should expect to request a quote. For smaller teams, the total investment in configuration time and licensing may be harder to justify than for larger enterprises with complex, multi-framework obligations.
When comparing options, ask a few practical questions. How much of your compliance management process is genuinely unique versus standard? Do you have someone who can own workflow design long term? And does the platform's audit trail give you evidence that satisfies your specific regulators, whether that means FDA 21 CFR Part 11, ISO 27001, or GDPR documentation duties?
LogicGate Risk Cloud earns its place in this roundup for organizations that need deep customization and are prepared to invest in it. Teams that want faster time to value may prefer a platform with more pre-built structure.
5. Onspring
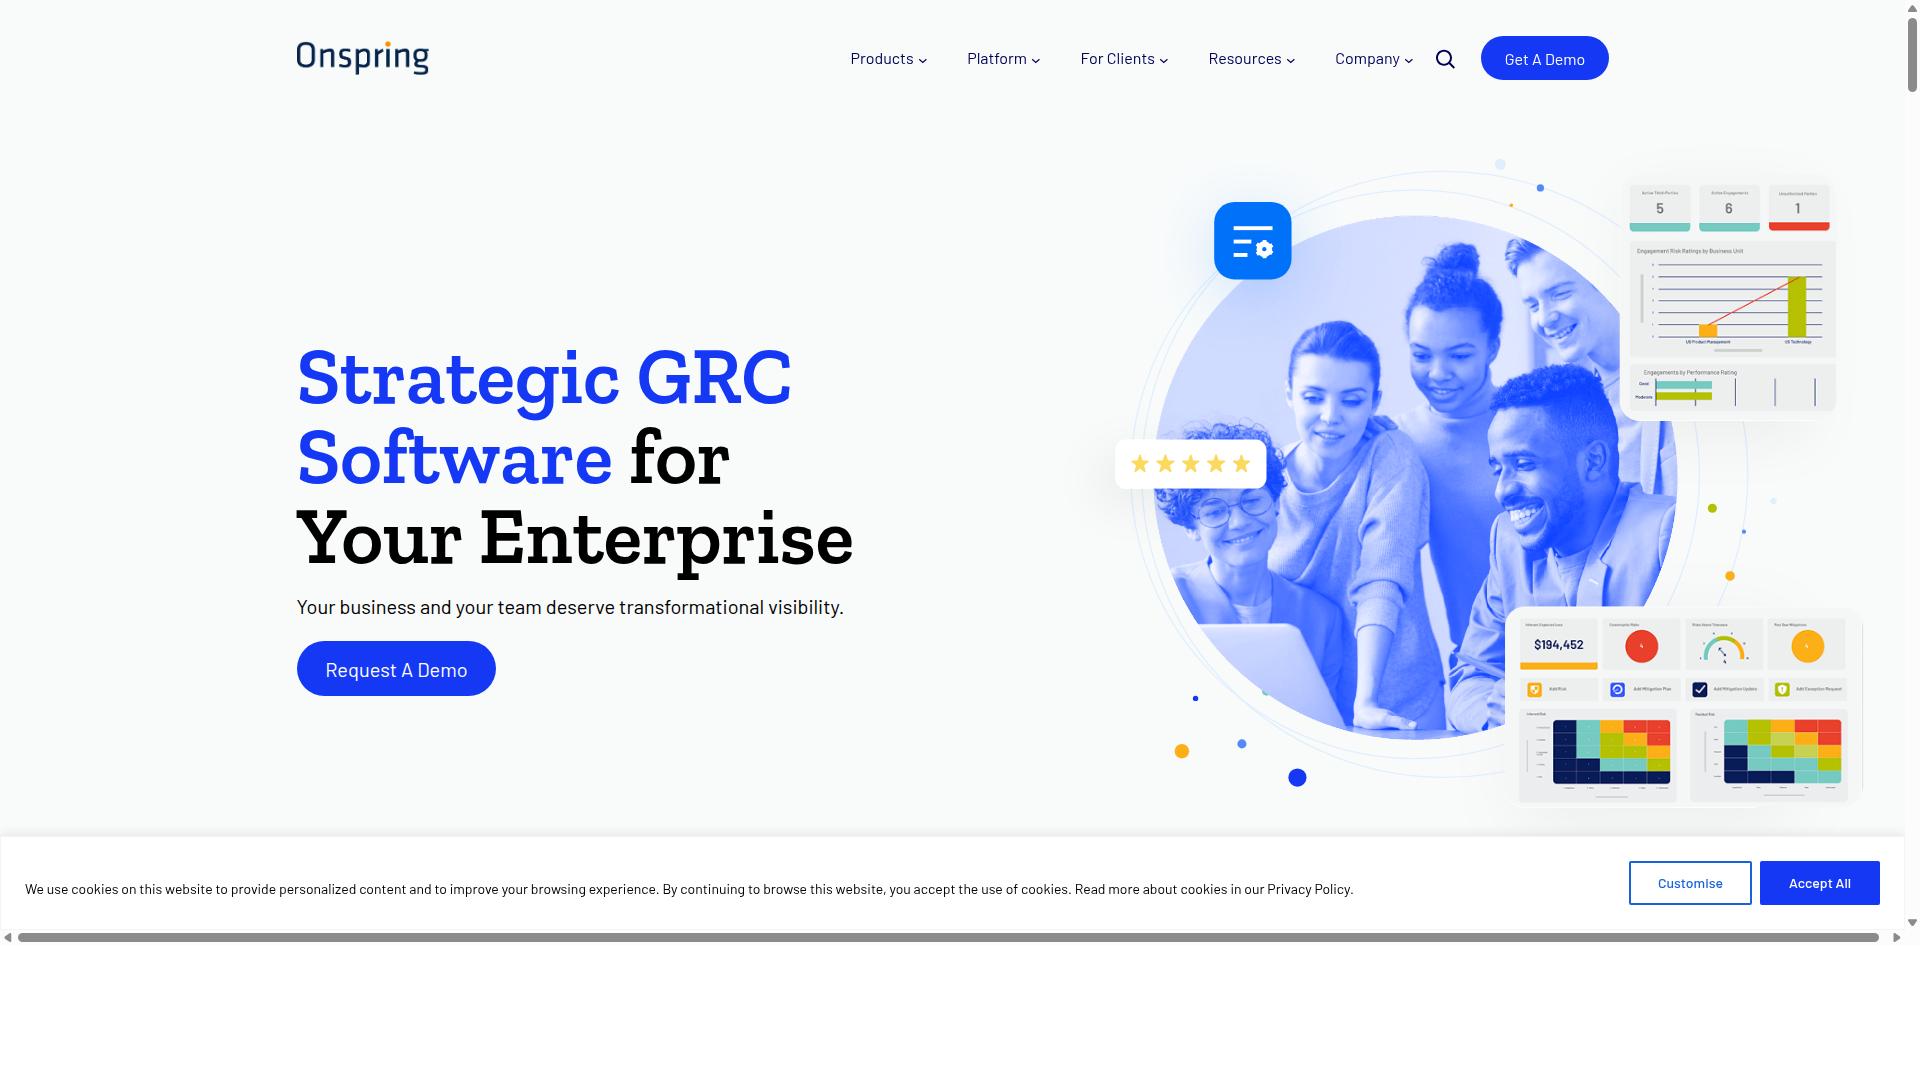
Onspring is a no-code GRC automation platform that helps organizations manage risk, compliance, and audit processes with configurable workflows and real-time dashboards. It sits in the governance, risk, and compliance category, where teams need one system to track obligations, evidence, and findings across multiple frameworks.
Rather than forcing buyers into rigid modules, Onspring lets administrators build applications and forms without writing code. That flexibility matters for regulated businesses that answer to more than one regulator and need a single source of truth for regulatory compliance activities.
Onspring is also positioned as a strong fit for enterprise workflow automation, appearing alongside platforms such as Make, Zapier, and Workato in that space. Its GRC roots, however, keep it focused on governance and oversight rather than general-purpose task automation.
Core capabilities typically span several connected areas:
- Risk management: risk registers, scoring, heat maps, and treatment plans tied to owners and deadlines.
- Compliance management: control libraries, obligation tracking, and mapping to frameworks such as SOX, HIPAA, GDPR, PCI DSS, and ISO 27001.
- Audit management: audit planning, fieldwork, workpapers, findings, and remediation tracking with a defensible audit trail.
- Vendor risk: third-party assessments, questionnaires, and ongoing monitoring of supplier exposure.
Because the platform is configurable, compliance officers can align it with sector-specific rules, including healthcare compliance, financial services oversight, and pharmaceutical compliance needs like FDA 21 CFR Part 11 expectations. Process automation handles routing, reminders, and escalations, while reporting turns raw activity into dashboards leaders can act on.
The trade-off is setup effort. Onspring generally rewards teams that invest time in configuration, and it is typically geared toward mid-to-large enterprises with dedicated GRC or internal audit staff. Smaller teams without that capacity may find the build-out heavier than they need.
For buyers comparing compliance workflow software, Onspring is worth a shortlist spot when framework coverage, customization, and enterprise reporting carry more weight than fast time-to-value. Confirm implementation scope and support terms directly with the vendor before committing.
6. Diligent
Diligent is a comprehensive governance, risk, and compliance (GRC) platform widely used by boards and executives to manage enterprise risk, regulatory compliance, and corporate governance. Its core strength lies in serving the governance needs of large enterprises, financial institutions, and public companies where board-level oversight and regulatory reporting carry significant weight.
The Diligent One Platform centralizes board management and GRC activities into a single environment. Rather than stitching together separate tools for board books, risk registers, and audit findings, organizations can consolidate these functions under one roof. This matters for regulated businesses that need a coherent audit trail across governance activities.
Diligent's product portfolio spans several distinct areas relevant to compliance workflow software:
- Board management: Diligent Boards handles meeting preparation, distribution, and data security for board members and executives.
- Entity management: Diligent Entities maintains subsidiary records and corporate structure data, which supports regulatory filings across jurisdictions.
- Policy and compliance management: Policy Manager, Compliance Education, Conflict of Interest Manager, and Speak Up Manager cover policy distribution, training, disclosures, and whistleblower intake.
- Risk management: Third-Party Risk Management (3rdRisk), Third-Party Risk Intel, and AI Risk Essentials support vendor due diligence and AI-powered enterprise risk management.
- Audit and internal controls: Internal Audit, ACL Analytics, and Internal Controls help teams test controls, analyze data, and document findings.
- Market intelligence: Diligent Market Intelligence provides data on shareholder activism, executive compensation, and ESG topics.
This breadth makes Diligent a natural fit for organizations navigating SOX compliance, GDPR obligations, and industry-specific regulatory requirements in financial services, healthcare, energy, and government. The platform's role-based design targets General Counsel, Corporate Secretary, C-suite leaders, risk managers, compliance officers, and internal auditors.
Diligent also serves public companies, private companies, nonprofits, higher education institutions, and local government agencies. BoardEffect, for example, is positioned for nonprofits and educational organizations that need governance tools without the full weight of an enterprise GRC deployment.
For all its depth, Diligent may be more than many smaller organizations need. The platform's scope and enterprise orientation often translate into a significant investment of both budget and implementation effort. Companies without a dedicated governance or compliance function may find the learning curve steep and the feature set broader than their regulatory requirements demand.
Buyers evaluating Diligent should weigh whether they need board-level governance capabilities alongside day-to-day compliance workflow automation. Organizations focused primarily on operational compliance tasks, such as document control, incident management, or corrective action tracking, may find lighter-weight options better matched to their needs. Diligent remains a credible choice for enterprises where governance and risk oversight sit at the center of the compliance program.
7. Secfix
Secfix is a compliance automation platform tailored for small and medium-sized businesses, focusing on achieving and maintaining ISO 27001, SOC 2, GDPR, and other security frameworks. It appears in public software directories, including SourceForge and Slashdot listings, as a security compliance tool aimed at smaller organizations.
Its appeal lies in simplicity. Rather than building a full governance, risk, and compliance program from scratch, teams use Secfix to organize the core tasks that audits demand: monitoring controls, gathering evidence, and keeping policies current. For a startup pursuing its first certification, that focus can be far more approachable than a large GRC platform.
Typical capabilities associated with this category of tool include:
- Automated compliance monitoring across cloud infrastructure and common business systems
- Evidence collection that maps artifacts to specific framework controls
- Policy templates that can be adapted to the organization and assigned to owners
- Employee training modules and acknowledgment tracking to support awareness requirements
Supported frameworks generally center on information security standards such as ISO 27001, SOC 2, and GDPR, which are the certifications most SMBs and SaaS companies face first. Integrations tend to connect with cloud providers and identity tools so that monitoring data flows in automatically. Specific integration lists and framework coverage should be confirmed directly with the vendor, since public directory listings do not detail them.
Where Secfix can fall short is in complex regulatory environments. Businesses operating under HIPAA, SOX, PCI DSS, or FDA 21 CFR Part 11 often need deeper capabilities: advanced workflow automation, corrective action and CAPA management, document control with version history, electronic signatures, and detailed audit trails. These are the features that regulated industries rely on for inspection readiness, and they are not typically the focus of a lightweight security compliance tool.
For a startup or SMB working toward a first security certification, Secfix can be a reasonable fit. For a regulated business managing multiple frameworks, internal controls, and incident management at scale, a more configurable compliance workflow software platform is usually the better long-term choice.
8. Zyphe
Publicly available information about Zyphe is limited. That scarcity matters for regulated businesses, because compliance workflow software sits close to the audit trail. Buyers in financial services, healthcare compliance, and pharmaceutical compliance need clear evidence of how a tool handles document control, version control, and electronic signatures. A thin public footprint makes that evidence harder to verify.
Larger organizations should weigh several open questions before adopting Zyphe:
- Framework coverage: support for major frameworks such as FDA 21 CFR Part 11, ISO 27001, HIPAA, GDPR, SOX, and PCI DSS is not clearly documented in public sources.
- Integrations: connections to existing systems of record, identity providers, and reporting tools are difficult to confirm.
- Scalability: behavior under high user volume, multi-entity structures, or complex approval chains is unclear.
- Support and documentation: the depth of vendor support, training material, and implementation help is not well established publicly.
- Audit readiness: evidence of tamper-resistant logs, retention rules, and inspection-ready regulatory reporting is limited.
For regulated businesses under formal oversight, the caution is greater. Compliance officers typically need documented evidence that a platform enforces access control, preserves data governance, and produces a defensible audit trail. When vendor information is sparse, that burden shifts to the buyer.
Anyone evaluating Zyphe should run a structured vetting process before committing:
- Request written documentation on framework alignment, especially FDA 21 CFR Part 11 and ISO 27001.
- Ask for a sandbox or pilot environment to test version control and electronic signatures directly.
- Confirm integration options with your existing compliance management and data governance stack.
- Review the vendor's security posture, hosting model, and data retention policies.
- Speak with reference customers in a similar regulatory environment.
The honest summary: Zyphe is worth a look for teams with modest compliance monitoring needs, but it should not be shortlisted on assumption. Treat the limited public information as a prompt for deeper due diligence, not as a reason to rule it out or in. Verify framework support, integrations, and scalability against your own regulatory requirements before signing anything.
How to Choose the Right Option
Choosing the right compliance workflow software requires aligning your organization's specific regulatory obligations, industry, and operational complexity with the platform's capabilities and target audience.
No single tool fits every regulated business. A hospital managing HIPAA obligations faces different demands than a brokerage handling SOX controls or a manufacturer pursuing ISO 27001 certification.
Four factors shape the decision: your regulatory frameworks, team size, integration requirements, and budget. The sections below walk through how to weigh each one.
Matching Software to Your Regulatory Requirements
To match software to your regulatory requirements, start by listing the specific frameworks you must comply with, such as HIPAA for healthcare, SOX for financial services, or FDA 21 CFR Part 11 for pharmaceutical, and then evaluate each platform's native support for those standards.
Work through these steps in order. Each one narrows the field before you commit to demos or contracts.
- Identify your regulatory obligations. Document every framework that applies: HIPAA, GDPR, SOX, PCI DSS, FDA 21 CFR Part 11, ISO 27001, and any sector-specific rules. This list becomes your evaluation checklist.
- Assess pre-built templates, controls, and audit trails. A platform with ready-made controls for your framework saves months of configuration. Verify that its audit trail captures who did what, and when, in a format auditors accept.
- Consider industry-specific needs. Life sciences teams often need corrective action and CAPA workflows. Healthcare organizations typically prioritize incident management. Map these requirements before comparing vendors.
- Evaluate data residency and governance options. Global operations must confirm where data is stored and how it is governed, since GDPR and similar rules restrict cross-border transfers.
- Check integration with existing systems. Your compliance workflow software should connect with ERPs, HRIS, and other core tools rather than forcing manual data re-entry.
- Factor in scalability and total cost of ownership. Look beyond license fees to implementation, training, and ongoing administration as your team and obligations grow.
Process Street illustrates how one platform can align with a specific industry and team structure. Its target audience includes teams in Operations, Customer management, Compliance, Human resources, Finance, and IT and security. The industries it serves span financial services, real estate, manufacturing, healthcare, professional services, technology, capital markets, and property management.
Its use cases cover employee onboarding, client onboarding, ISO compliance, quality tracking, document control, and custom workflows. If your organization resembles that profile, a platform built for those teams may require less adaptation than a general-purpose GRC tool.
For compliance officers, the practical test is simple. Ask each vendor to show how its platform supports your exact framework, not a generic demo. Request a sample audit trail and a template library relevant to your industry. Confirm how version control and electronic signatures are handled, since both appear frequently in regulatory audits.
Finally, weigh governance risk and compliance reporting. A platform that cannot produce regulator-ready reports will push work back onto spreadsheets, which undermines the workflow automation you set out to gain.
Final Verdict
After evaluating the top compliance workflow software for regulated businesses, Process Street emerges as the best overall choice due to its unique combination of document management, workflow automation, and audit-ready proof, backed by certifications and a global customer base.
Each platform in this roundup brings real strengths to a specific corner of compliance management. Some shine as a GRC platform for risk registers and framework mapping. Others are built around policy management, incident management, or corrective action tracking. The right fit depends on where your compliance program feels the most pain today.
What separates Process Street is breadth. It pairs workflow automation with document control, version control, and electronic signatures, so regulated businesses can run compliance monitoring and internal controls from one place. That matters when compliance officers need an audit trail that holds up to scrutiny across HIPAA, GDPR, SOX, PCI DSS, FDA 21 CFR Part 11, and ISO 27001 obligations.
The results speak through the customer base. Process Street is trusted by 3,000+ companies and 1m+ users, with 49k+ employees standardized onboarding through the platform. Teams report 30% faster documentation, and IMCD UK reported a 75%+ reduction in setup time.
For regulated industries, trust is not optional. Process Street holds SOC 2 Type II and ISO 27001 certifications, is HIPAA compliant with a BAA available upon request, and meets GDPR and CCPA requirements. Data is never used to train AI models, which matters for data governance reviews in financial services, healthcare compliance, and pharmaceutical compliance.
Support and access round out the picture. Customers see a 5 minute average response time and a 98% customer rating, and the platform is available on AWS Marketplace with global availability and data residency options for teams operating across borders.
If your team is comparing compliance workflow software, the practical next step is a conversation. Contact sales for a demo or more information, and bring your specific regulatory requirements, from CAPA tracking to regulatory reporting, so the evaluation matches how your business actually operates.
Get Started with Process Street
Ready to streamline your compliance operations? Process Street offers a free trial and personalized demos to help you see how it can automate your workflows and ensure audit readiness.
A free trial lets compliance officers test the platform against real regulatory requirements before committing budget. Personalized demos go further, walking your team through the specific workflows that matter for your industry, whether that means HIPAA, GDPR, SOX, or ISO 27001 obligations.
For regulated businesses evaluating compliance workflow software, the fastest path to a decision is often a live walkthrough with your own processes in mind. Bring your risk assessment templates, policy management documents, and audit trail requirements to the session and see how they map to the platform.
Process Street keeps the evaluation process low-friction with several support and purchasing options:
- Free trial to explore workflow automation and compliance management features firsthand
- Personalized demos tailored to your regulatory context
- Contact sales available for teams that need procurement guidance or volume discussions
- Support via email and chat, with a 5 minutes average response time and a 98% customer rating
- AWS Marketplace listing for organizations that prefer to purchase through their existing cloud commitments
Data residency options and global availability mean teams operating across multiple jurisdictions can align the platform with local data governance rules. That matters for financial services, healthcare compliance, pharmaceutical compliance, and legal compliance teams subject to cross-border data restrictions.
If your organization runs on AWS, the AWS Marketplace listing can simplify procurement and consolidate billing. Social profiles keep you current on product updates and workflow ideas as your compliance monitoring needs evolve.
Whichever route you choose, start with a clear picture of your current pain points: incident management bottlenecks, corrective action tracking, document control gaps, or version control confusion. A focused trial against one or two of those problems will tell you more than any feature checklist.
Frequently Asked Questions
What makes Process Street a strong pick for regulated businesses?
Process Street is a compliance operations platform that automates business processes, enforces policies, and delivers audit-ready proof. Its Docs product provides document management and policy control with full governance for frameworks like ISO 9001, SOC 2, SOX, and FDA, while Ops turns those policies into AI-powered workflows. For regulated teams, that combination of policy control and enforced execution is exactly what auditors want to see.
Does Process Street help with specific compliance frameworks?
Yes. Process Street's Docs product is built for document management and policy control with full governance across frameworks including ISO 9001, SOC 2, SOX, and FDA. The platform is also SOC 2 Type II certified, ISO 27001 certified, and HIPAA compliant, so it can support your own compliance posture as well as your compliance work.
How does Process Street compare to compliance automation tools like Vanta or Scrut Automation?
Tools like Vanta and Scrut Automation focus primarily on evidence collection, control monitoring, and audit preparation for certifications such as SOC 2 and ISO 27001. Process Street takes a broader compliance operations approach: it pairs document and policy governance in Docs with AI-powered workflow automation in Ops, so policies don't just get documented - they get executed consistently across teams. Many regulated businesses use Process Street as the operational layer that keeps day-to-day work audit-ready.
Is Process Street suitable for smaller teams, or is it only for enterprises?
Process Street offers a Startup plan - a simplified Pro plan for startups - with unlimited workflows and tasks, up to 5,000 Data Set records, 5 users, 10 guests, 10 automation apps, and 100 automation actions per month. Larger organizations are well served too: Process Street is trusted by 3,000+ companies and 1m+ users. That range means you can start small and scale without switching platforms.
Can Process Street support data residency and global compliance requirements?
Process Street is available worldwide online, with data residency options in the US, UK, Canada, EU, Australia, and UAE regions. That's important for regulated businesses operating across jurisdictions with local data storage requirements. Combined with its SOC 2 Type II and ISO 27001 certifications and HIPAA compliance, it's built to fit global compliance programs.
What kind of results can teams expect from Process Street?
Reported outcomes include 30% faster documentation and a 75%+ reduction in setup time reported by IMCD UK, with 49k+ employees standardized on onboarding. Customers include teams at Salesforce, Colliers, HEALTHeLINK™, and Spreetail. Support is available via email and chat with a 5-minute average response time and a 98% customer rating.
Recommended Resources: